

The short version
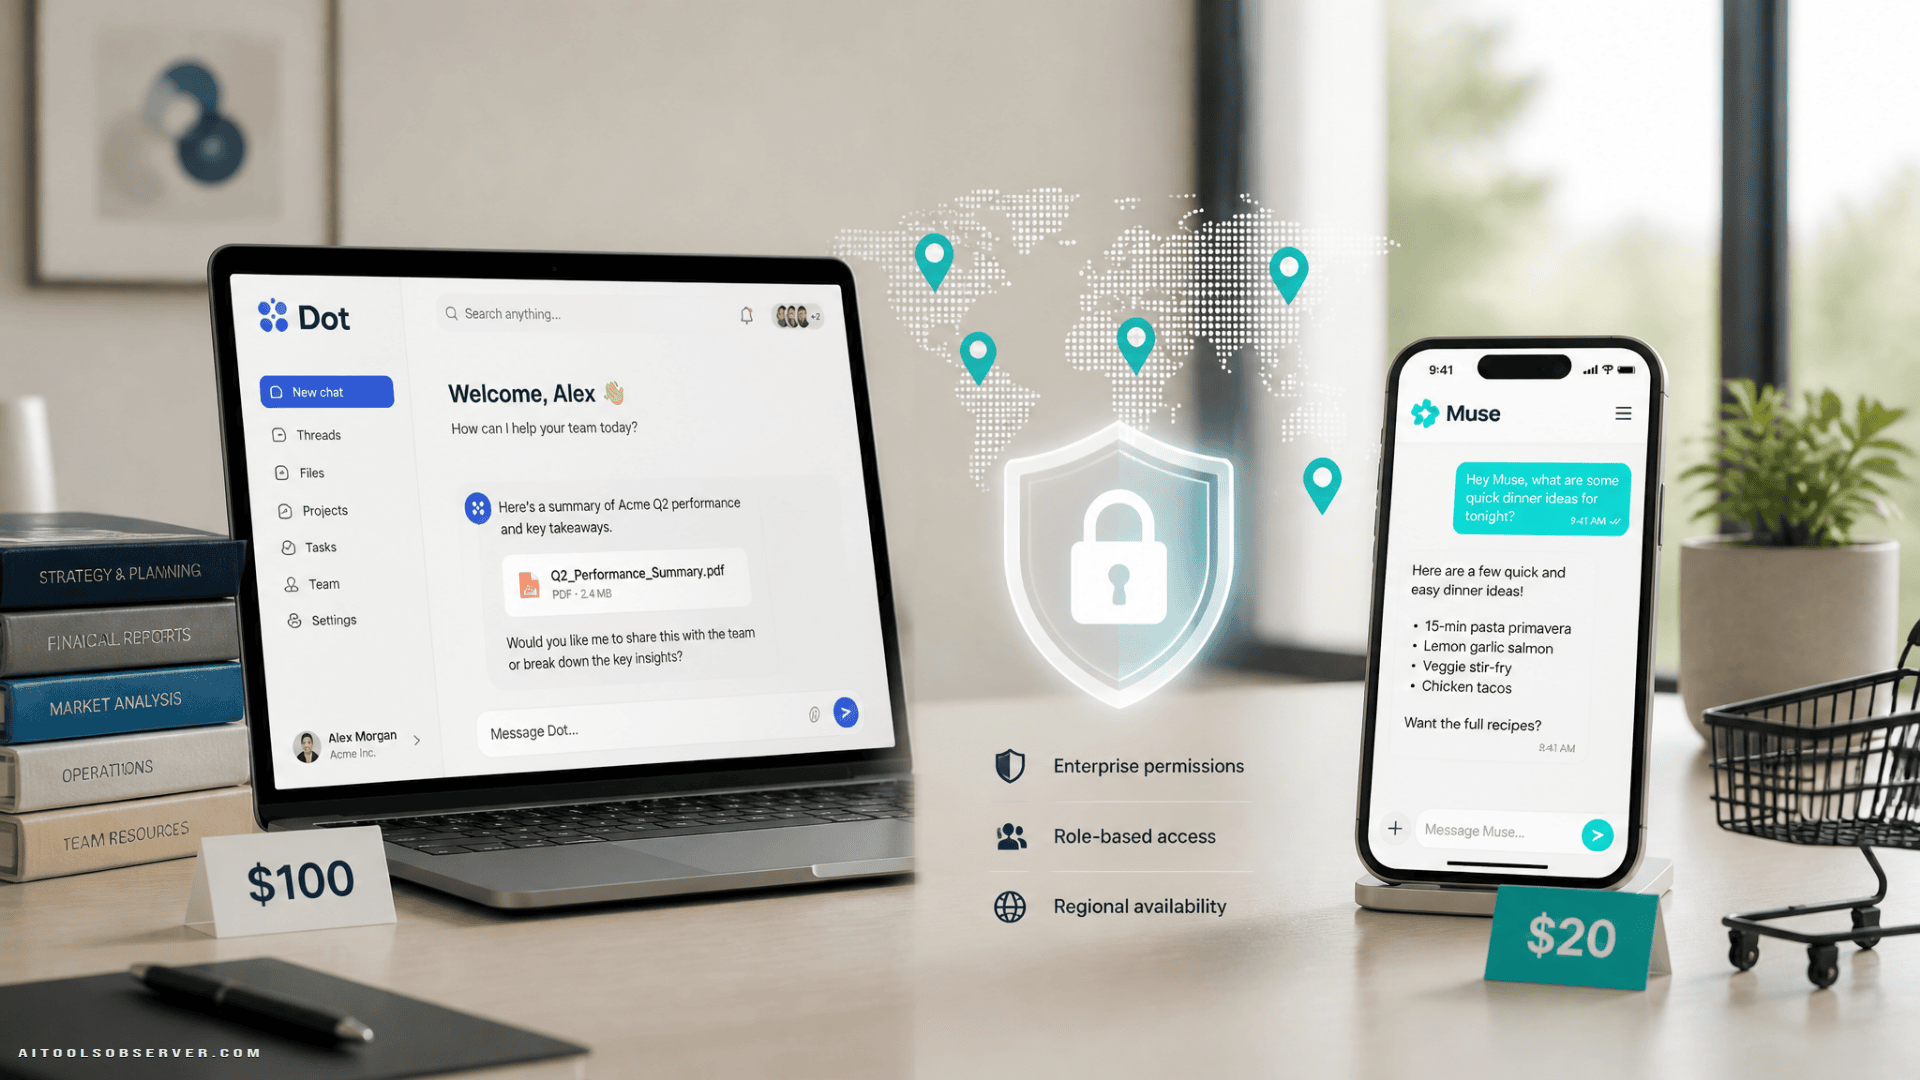
Muse looks easier to try and easier to understand for individual users. It is available through dedicated apps, the web, and WhatsApp, and its pricing starts far below Dot’s current entry point.
Dot appears more tightly integrated into OpenAI’s broader work stack. It lives inside ChatGPT, works with connected tools, supports recurring jobs, and is positioned for users who want an agent tied into research, workflows, and business environments.
The tradeoff is straightforward:
- Muse is the lower-friction option, at least on price and consumer-style access
- Dot is the more workflow-centric option, but with a higher cost of entry
- Both require careful thought about permissions and linked accounts
- Availability may eliminate one choice before features do
Both are framed as always-on AI agents rather than simple assistants.
What these agents are actually designed to do
The shared promise is simple: give the agent a task, then stop babysitting it. In practice, that means these systems are meant to perform multi-step work in the background.
Muse is described as handling tasks like:
- shopping
- completing forms
- making travel plans
- sending emails
- monitoring prices
Dot is described more as an ongoing work agent for:
- research tasks
- recurring work
- connected app workflows
- tasks inside the wider ChatGPT, Work, and Codex ecosystem
That distinction matters. Muse appears consumer-first in its framing, while Dot appears more embedded in professional knowledge work.
Environment and access model
One of the clearest differences is where the agent “lives.”
Muse runs on a dedicated secure virtual machine with its own browser. The experience is meant to resemble messaging another person, which makes it approachable for users who do not want to manage a complex agent setup.
Dot lives within ChatGPT. Each Dot has its own cloud computer, can use connected plugins, remembers relevant context, and can keep working on scheduled or recurring jobs. OpenAI also allows users to grant a Dot access to their local computer for retrieving files or browsing the web.
That last point is important. Local computer access changes the risk profile. A cloud-only agent that acts inside its own contained environment is one thing; an agent that can touch your local files or browse on your behalf is another.
Pricing: the biggest practical divider
For many users, the comparison stops here.
Muse has a free tier with a usage cap, plus paid tiers at $20 per month and $100 per month. Dot, by contrast, currently starts much higher. The lowest available option for individuals is Pro 100 at $100 per month, while Business Premium is priced at $100 per user per month billed annually or $125 per user per month billed monthly.
What that means in practice
Muse is much easier to test without making a large commitment. That makes it better suited to curiosity, light personal automation, and early experimentation.
Dot’s pricing suggests a different buyer. At current entry levels, it is harder to justify as a casual consumer tool. It makes more sense when the user already lives in ChatGPT-based workflows or when the agent is expected to support repeatable business tasks.
A simple way to think about it:
- Choose Muse if low-cost experimentation matters
- Choose Dot if tighter integration with OpenAI’s work environment matters enough to justify the premium
Permissions and autonomy: where trust gets tested
Always-on agents become useful only when they are allowed to do things. That is also where they become uncomfortable.
Meta states that Muse asks for permission before taking sensitive actions such as sending an email or making a purchase. OpenAI uses a mix of permissions, Custom Rules, and Auto-review to govern what Dots can do. OpenAI also notes that proactive Dot research remains read-only until a later action passes normal permission checks.
This is not just a UX detail. It defines how much supervision the system still needs.
Muse’s permission posture
Muse appears to use direct approval prompts, including options such as allowing a single action or always allowing a class of actions. For a user, that can feel intuitive. You see the action, approve it, and move on.
The risk is that “always allow” settings can quietly widen the agent’s operating room over time. That is convenient, but it should be granted sparingly.
Dot’s permission posture
Dot’s system appears more policy-oriented. Custom Rules and Auto-review suggest a structure that can be tuned over time, especially for users who want repeatable behavior across recurring tasks.
That may be better for formal workflows, but it also means setup discipline matters more. A poorly configured recurring agent can repeatedly do the wrong thing faster than a one-off assistant.
Privacy defaults: not just policy, but starting conditions
Both products ask for trust, especially once email, calendars, files, and browsing sessions enter the picture.
Meta states that conversations and data within Muse’s VM are not shared with its advertising systems, and that users can choose not to have interactions used to improve Meta’s AI models. At the same time, reporting on early hands-on use found model-improvement settings enabled by default, along with a permission setting that prompted for only some actions.
OpenAI states that activity from personal-plan Dots may be used to improve models depending on the user’s ChatGPT setting. Business and Enterprise data is not used for training by default.
Why defaults matter more than settings pages
Most users do not thoroughly configure privacy controls on day one. They use the product as presented. That means defaults deserve more attention than the existence of an opt-out.
From a practical standpoint:
- Muse appears to require a close look at default sharing and permission behavior before serious use
- Dot requires checking which ChatGPT data controls apply to your plan and agent activity
- Business buyers should weigh default business privacy terms more heavily than feature lists
If the agent will touch personal mail, children’s documents, travel bookings, or internal work material, this should be treated as a deployment decision, not a convenience feature.
Connected services and real-world usefulness
Both tools become more useful as they connect to more systems. They also become more sensitive.
Muse can be linked with services like email and calendar, and examples suggest it can organize saved content and act across practical consumer workflows. Dot can work across connected applications, retrieve local files if allowed, and is being integrated closely with ChatGPT, Work, and Codex.
The tradeoff is predictable:
- more connected services means more capable execution
- more connected services also means broader access to sensitive data and actions
This is where many AI agent demos look impressive but real deployment slows down. People do want automation. They do not want an agent loose inside everything. Some users may prefer approaches built around full privacy and data control.
Platform access and regional availability
Availability is not a footnote here. It may be the deciding factor.
Muse is currently available in the US and Canada.
Dot has a more segmented rollout. It is rolling out to eligible Pro users outside the EEA, Switzerland, and the UK. Business Premium users can access Dots across supported ChatGPT regions, while Enterprise access remains in beta.
Deployment implications
This creates a very different buying path for each product.
Muse is geographically narrower, but simpler to understand: if you are in the US or Canada, you can consider it.
Dot’s availability depends not only on geography but also on plan type. A personal user may find the product excluded by both region and subscription level, while a business team may have access through a supported ChatGPT business plan.
For buyers comparing the two, this means “feature parity” may not matter if one product is unavailable to your team, region, or account class.
Friction in actual use
The appealing phrase is “always-on.” The realistic phrase is “always-on, with supervision.”
Both companies caution that their agents can make mistakes. That warning is not boilerplate. It affects how you should deploy them.
A few practical examples:
- An agent monitoring prices is relatively low risk
- An agent drafting research or collecting information is moderate risk
- An agent sending messages, making purchases, moving files, or handling forms is higher risk
- An agent with local file access or broad account connections needs stricter review rules
There is also the issue of external limits. Even if the agent is technically capable, websites and services may not welcome it. Amazon, for example, has already blocked Muse from shopping on its site. That matters because many consumer agent pitches assume the open web will cooperate.
As capability expands into broader access to sensitive data and actions, deployment friction tends to increase.
Muse is the better fit if you want:
- a lower-cost way to try an always-on agent
- consumer-friendly interfaces like apps, web, or WhatsApp
- task flows around shopping, planning, messaging, or lightweight organization
- a more direct, approval-based interaction model
Dot is the better fit if you want:
- deep alignment with ChatGPT workflows
- recurring work tied to research, apps, and structured business tasks
- more policy-like control over what the agent can do
- business-plan privacy defaults that are clearer for organizational use
The real decision: cost versus control surface
It is tempting to frame this as Meta versus OpenAI, but that is not the useful comparison. The useful comparison is simpler: how much autonomy do you need, and how much control surface are you prepared to manage?
Muse looks like the more accessible entry point into persistent agents. Dot looks like the more serious workflow operator, but one that demands a larger budget and more deliberate governance.
If you are choosing today, start with constraints before capabilities:
- Check whether the product is available in your region and account tier.
- Decide whether consumer tasking or work-stack integration matters more.
- Review permission defaults before linking email, calendar, files, or browser access.
- Treat recurring autonomy as a policy question, not just a feature.
That sequence will save you more time than comparing agent demos.



Comments (0) No comments yet
Want to join this discussion? Login or Register.
No comments yet. Be the first to share your thoughts!