


The Approval Trap
Here’s how it plays out in practice.
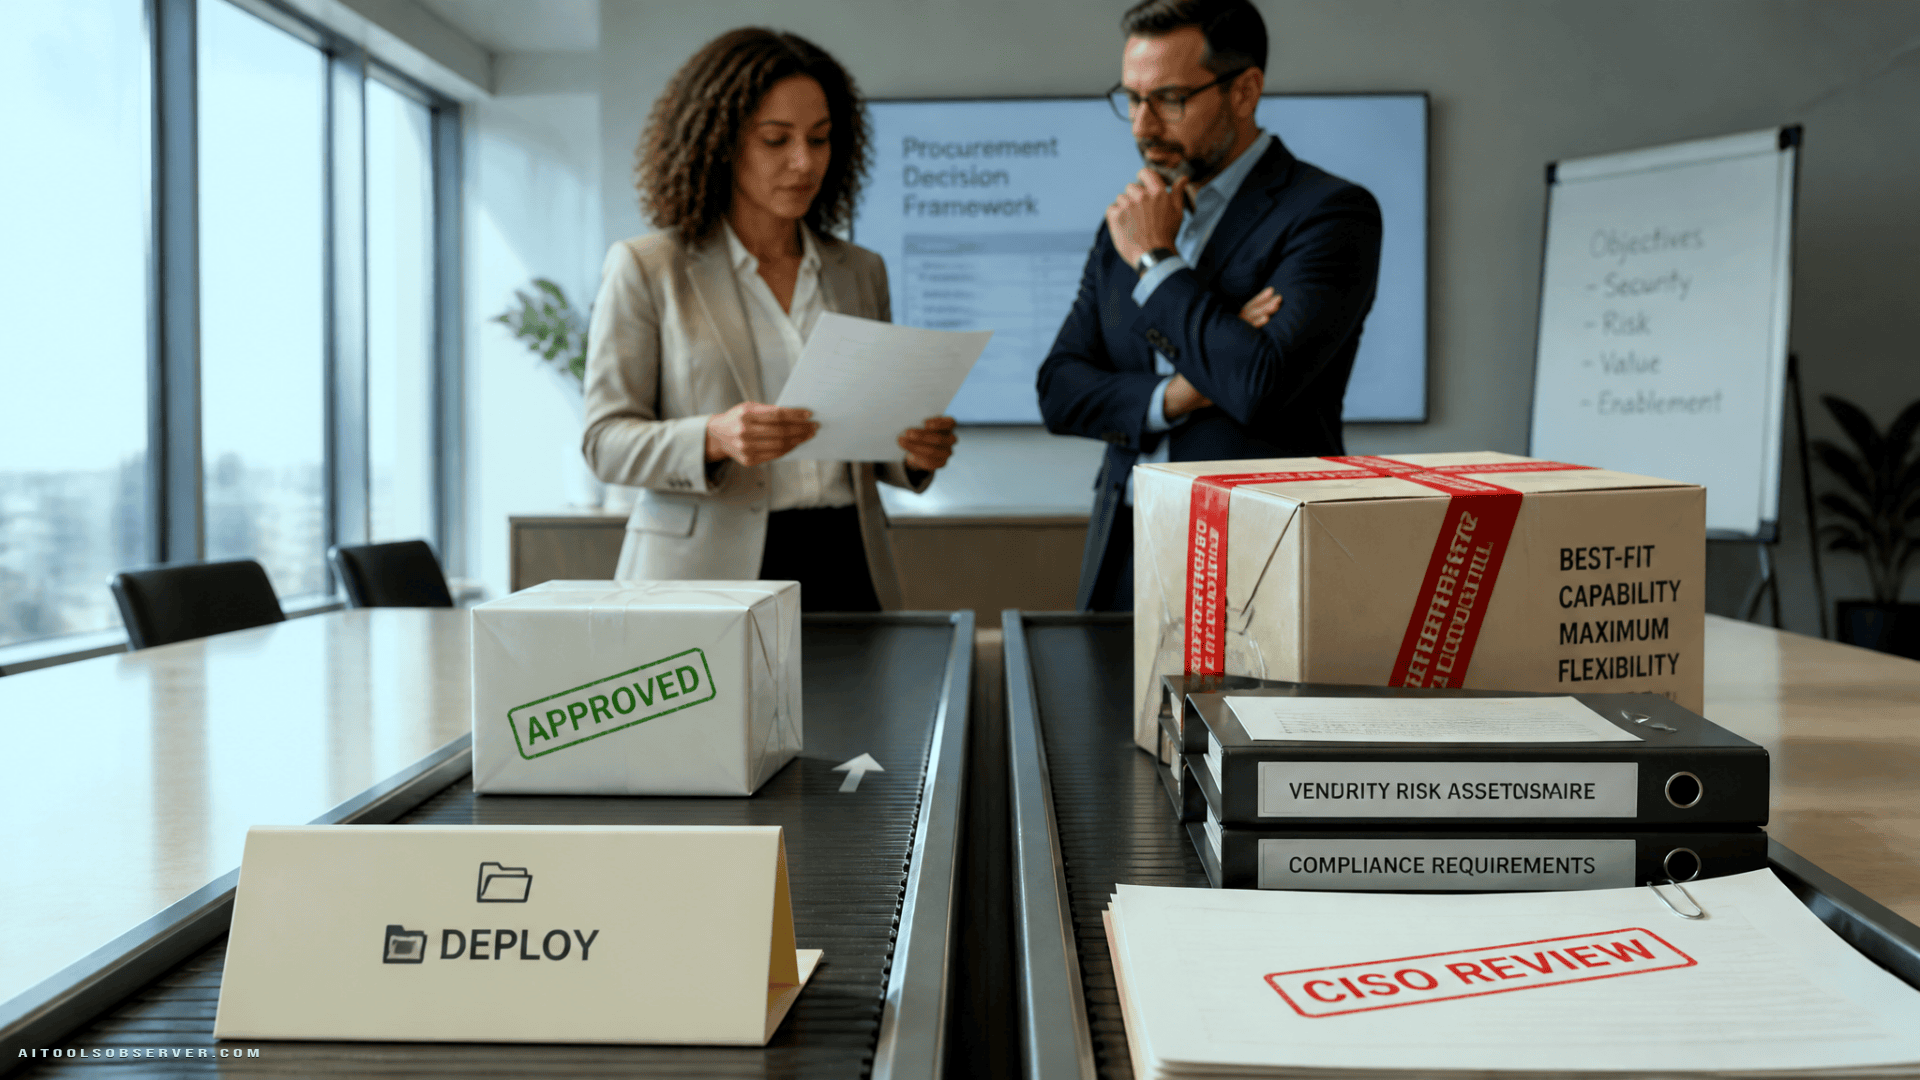
A pre-packaged agentic AI tool that slots neatly into your existing compliance posture is attractive. It doesn’t trigger a hard CISO review. It doesn’t demand unfamiliar vendor terms. It doesn’t require new security controls. It just… gets approved.
The more capable alternative might require new governance frameworks, a longer security review, and conversations your procurement team hasn’t had before. So it stalls. Or gets quietly dropped.
The result: organizations end up deploying agents that are easy to govern rather than agents that are fit for purpose. That’s a fundamental inversion of good decision-making.
Why This Is a Bigger Problem Than Vendor Lock-In
Vendor lock-in gets a lot of attention in enterprise AI conversations. It’s a legitimate concern — as integrations deepen and organizational dependence grows, switching costs rise.
But the Actuaries Institute report argues the deeper risk is more immediate: choosing capability-limited tools because they generate no friction.
A pre-packaged agent that lacks the capabilities required for a specific task can’t be fixed by layering on more controls. You can add governance. You can add monitoring. You can add human review checkpoints. But if the underlying model can’t perform the task to the required standard, none of that changes the outcome.
This is the part that often gets glossed over in procurement conversations — the assumption that governance can compensate for capability gaps.
What Good AI Governance Actually Looks Like
The report is clear on this: the goal is not to select the system that is easiest to govern. It’s to select the system that best meets the business need, then implement governance proportionate to the risks that system creates.
That’s a meaningful distinction. It means:
- Governance should follow capability decisions, not precede them
- Controls should be calibrated to the specific use case, not applied uniformly across all AI deployments
- Risk appetite matters — what’s acceptable in a low-stakes internal workflow is not acceptable in a customer-facing claims process
Applying the same compliance template to every AI deployment regardless of context is both inefficient and misleading. It creates the appearance of governance without the substance.
The Monitoring Problem at Scale
Agentic AI is built to handle volume. That’s the point. But volume creates a monitoring challenge that most organizations aren’t fully prepared for.
The report highlights a specific dynamic worth understanding: even a stable error rate produces more absolute errors as throughput increases. If your AI agent processes ten times more interactions, a 1% error rate means ten times more errors in real terms — even though the rate hasn’t changed.
Quality assurance systems designed for human-scale operations don’t automatically scale to handle this. The report’s framing is precise: organizations need to strengthen quality assurance as throughput increases, not just scale it.
What to Watch For
Two early warning signals the report specifically calls out:
- Claims wrongly rejected by an AI system and later overturned — a potential indicator of model performance problems
- Customer documents containing another person’s information — a potential indicator of cybersecurity or data privacy failures
These aren’t hypothetical edge cases. They’re the kinds of errors that surface when agentic systems operate at volume without adequate monitoring infrastructure.
The Human Review Dilemma
There’s an obvious tension here. If you’re deploying an AI agent to handle volume, requiring human review of every interaction defeats the purpose.
The report acknowledges this directly. The answer isn’t blanket human oversight — it’s accessible, timely, and effective dispute resolution mechanisms. When errors occur at scale, the number of disputes can spike quickly. Internal and external resolution pathways need to be ready for that reality before deployment, not retrofitted after the first wave of complaints.
What This Means for Tool Selection
If you’re evaluating agentic AI tools right now — whether for customer service, claims processing, document handling, or any other high-volume use case — the procurement dynamic described here is worth taking seriously.
A few practical implications:
- Don’t let the approval process drive the capability decision. If a more capable tool requires harder governance work, that work is usually worth doing.
- Evaluate tools against the specific task, not against a generic compliance checklist. A tool that clears review easily but underperforms on the actual use case is not a safe choice — it’s a deferred problem.
- Build monitoring infrastructure before you scale. The time to design quality assurance and dispute resolution is during deployment planning, not after errors start surfacing.
- Treat vendor lock-in as a secondary concern, not the primary one. Capability fit comes first.
The real risk in agentic AI procurement isn’t choosing the wrong vendor. It’s optimizing for the wrong criteria — and not realizing it until the system is already embedded in your operations.
The tools that are easiest to approve are not always the tools that will perform. Knowing the difference, and being willing to do the harder governance work for the right solution, is what separates organizations that use AI well from those that just use AI.


Comments (0) No comments yet
Want to join this discussion? Login or Register.
No comments yet. Be the first to share your thoughts!