


What’s Actually in the Release
The launch covers several distinct product areas, each targeting a specific operational problem.
Workflow automation via Duo Agent Platform — New goal-driven flows, accessible through /goal in Duo CLI, headless mode, Duo Agentic Chat, and a GitLab for Slack integration, are designed to move work across coding, review, testing, security checks, and deployment under one identity and policy framework. Custom Flows and flow triggers let teams automate multi-step sequences without losing the audit trail.
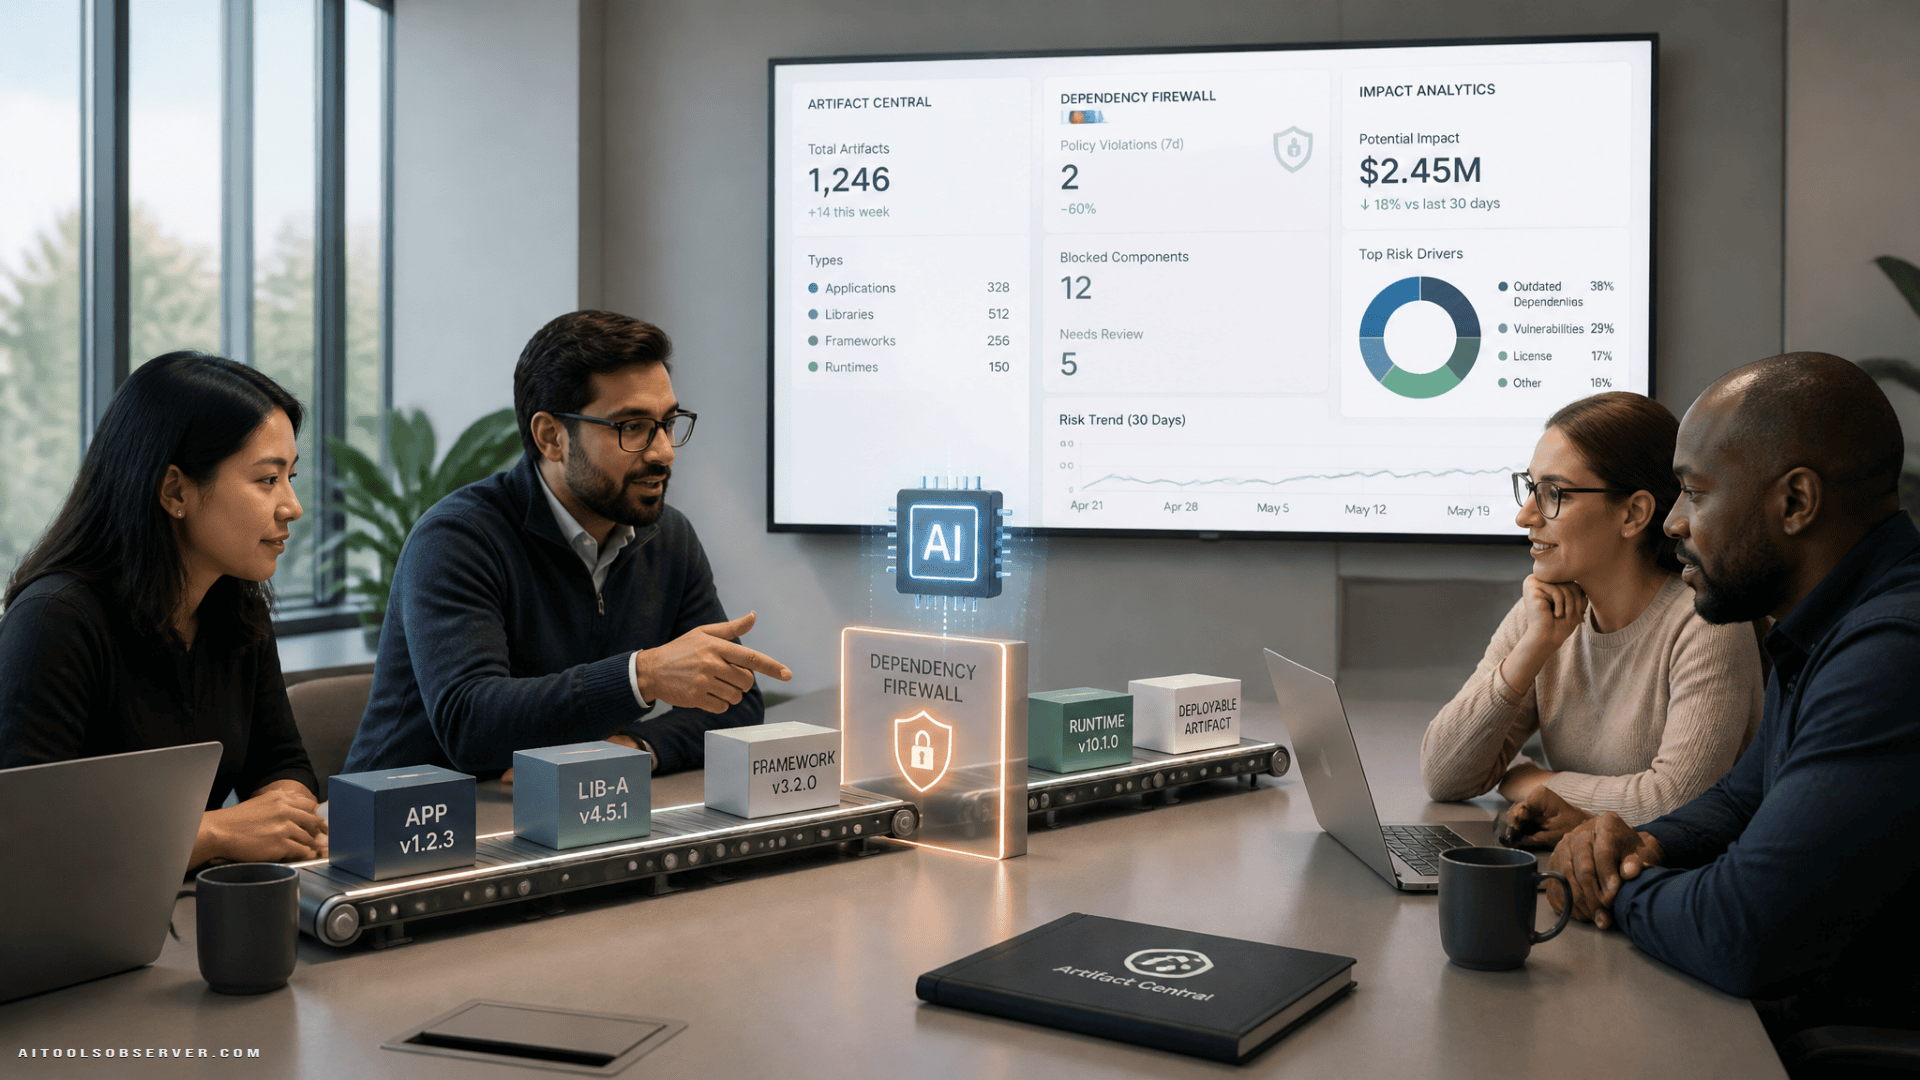
GitLab Artifact Central (beta) — A new control plane that consolidates containers and packages alongside source code management and CI pipelines. Platform teams can set policy at the organisation level and track what has been published, reducing the risk of builds pulling incorrect or missing components from open-source packages and base images.
GitLab Dependency Firewall (early access) — Checks packages against configurable policy rules before they enter a build. Rules can cover package age, vulnerability severity, malicious package detection, and licence compliance. Teams can configure responses to warn, block, or quarantine packages.
GitLab Secrets Manager (generally available) — Stores build-time secrets centrally, limits access to the specific job requiring each credential, and logs activity in the audit trail. It is now available on GitLab.com and GitLab Self-Managed in the 19.5 release.
Security flows using Anthropic models — New Duo Agent Platform security flows integrate Anthropic’s Claude Mythos 5 and 5.1 models, aimed at identifying vulnerabilities and verifying fixes within existing development workflows.
GitLab Security Standard — A published framework setting out five controls for agentic software development, using time from detection to verified remediation as its primary metric.
Duo Agent Platform Impact Analytics (early access) — Provides visibility into AI cost and impact by team, task, and model. Administrators can set spending ceilings at subscription, group, or user level.
The Governance Problem Behind the Launch
The underlying tension GitLab is responding to is real and increasingly common in large engineering organisations. As agentic development workflows scale, the question of who — or what — approved a given change, and at what cost, becomes difficult to answer without deliberate tooling.
GitLab’s Chief Product and Marketing Officer Manav Khurana put it plainly: most enterprises already run a software factory, but few have intentionally designed the systems and controls governing it. The new tooling is an attempt to make governance a structural property of the platform rather than a process bolted on afterward.
The Dependency Firewall and Artifact Central together address the supply chain angle specifically. Software builds that pull from uncontrolled external sources introduce risk that is easy to overlook until something goes wrong. Centralising artifact policy and enforcing it before packages enter a build is a more defensible posture than scanning after the fact.
AI Cost Visibility Is a Distinct Problem
One aspect of this release worth noting separately is the focus on AI spending accountability. Impact Analytics is not a security tool — it is a management tool. It exists because organisations consuming AI credits at scale often cannot connect that consumption to measurable outcomes.
The ability to set spending ceilings at the group or user level, and to see cost broken down by team and task, gives engineering leaders a mechanism to prioritise use cases based on evidence rather than assumption. That is a practical concern that tends to surface once AI adoption moves past the pilot stage.
Context and Scale
GitLab reports that active users of agentic software development on the platform grew 200% year on year over the past three months, with secure repositories up 100% and CI/CD pipelines up 40%. GitLab Orbit, the platform’s real-time knowledge layer for agents, has been used by more than 3,500 organisations and has handled over 280,000 queries from coding agents since its beta.
These figures, as reported by GitLab, suggest the governed software factory framing is not purely aspirational — the underlying usage patterns are already present and growing.
Who This Is For
This release is most directly relevant to enterprise DevSecOps teams managing complex, multi-team software pipelines where AI-generated code is becoming a meaningful share of output. The tooling is also relevant to platform engineers responsible for artifact and dependency management, and to engineering leaders who need to account for AI investment at the organisational level.
Teams running smaller, simpler pipelines will find less immediate value here. The governed software factory concept is designed for environments where the coordination and compliance overhead is already a real cost.
Practical Takeaway
The most useful way to read this release is as GitLab’s answer to a specific maturity problem: what happens to governance, security, and cost accountability when AI agents start doing a significant share of the work? The tooling introduced here — particularly Dependency Firewall, Artifact Central, and Impact Analytics — addresses that question with concrete mechanisms rather than policy recommendations. Whether the implementation delivers on that promise will depend on how well these components integrate in practice, but the problem they are targeting is well-defined and increasingly urgent.

Comments (0) No comments yet
Want to join this discussion? Login or Register.
No comments yet. Be the first to share your thoughts!