


What changed
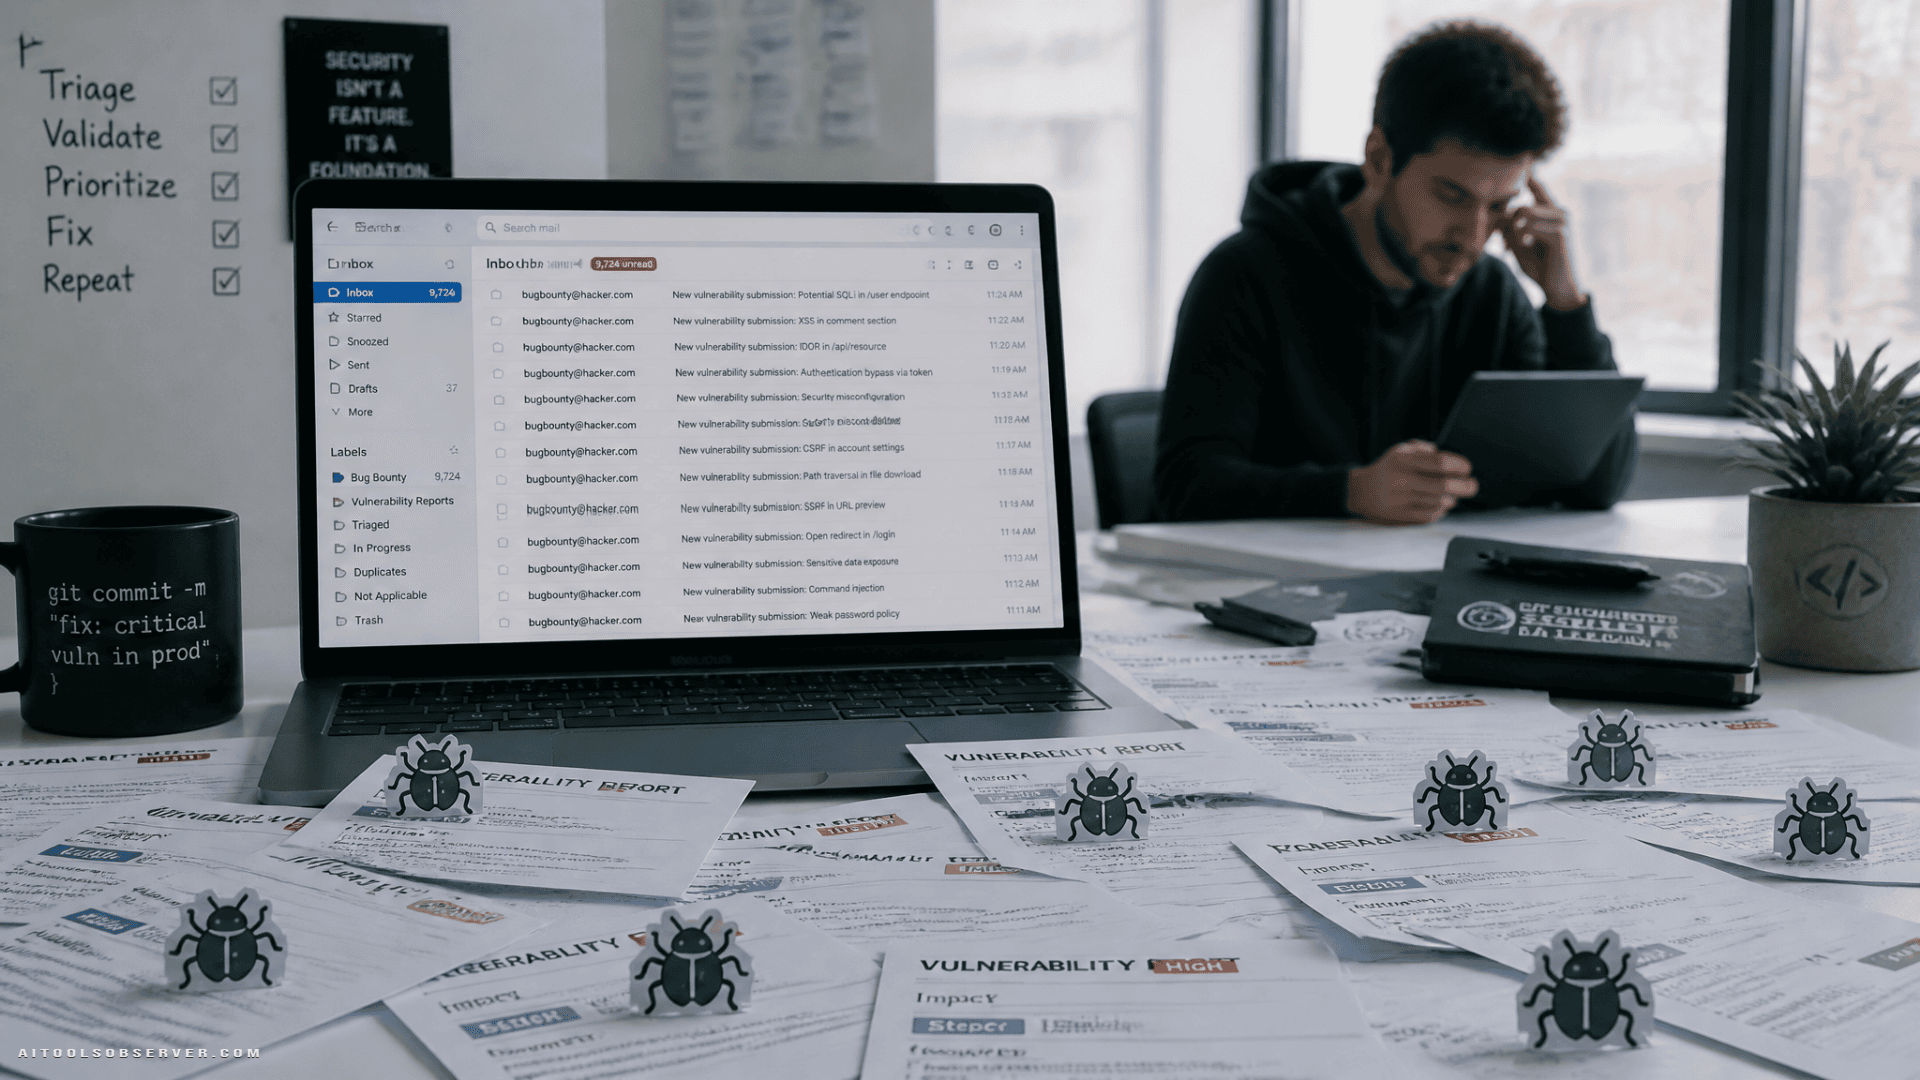
Google paused the program as of October 1 and said it plans to provide an update in the first quarter of 2027. Based on the available context, the company linked the decision to a surge in automated and low-quality reports.
Reports describing hallucinated vulnerabilities are especially costly. They still need to be reviewed, understood, and dismissed, which consumes time from engineers and open source maintainers who are already limited resources.
Participants were reportedly directed toward Google’s other bug bounty programs in the meantime. That suggests the pause is targeted, not a broader retreat from coordinated vulnerability disclosure.
Why AI-generated reports are a real problem
This is not simply a matter of spam volume. The deeper issue is credibility at scale.
Bug bounty systems work when researchers submit findings that are:
- technically grounded
- reproducible
- scoped correctly
- worth a human reviewer’s time
AI-generated reports can fail on all four points at once. A polished write-up may look convincing while describing a vulnerability that does not exist, misunderstands the codebase, or invents an exploit path. That makes filtering harder, not easier.
For open source programs, the risk is sharper. Review work often falls on maintainers who may not have large internal security teams behind them. Every invalid report competes with real engineering, patching, and release work.
Why this matters beyond Google
Google is large enough to absorb more noise than most organizations. If even a major company pauses a program because of automated submissions, smaller vendors and open source projects should pay attention.
The broader lesson is that AI lowers the cost of producing a plausible-looking security report. It does not automatically raise the quality of the underlying research. That gap creates pressure in several places:
- intake systems that were built for human-scale submissions
- security teams that must verify claims before acting
- maintainers who are pulled into false investigations
- legitimate researchers whose reports may face slower review
In other words, AI can increase output faster than programs can increase verification capacity.
What this means for security teams
Teams running disclosure or bounty programs may need to tighten their process. The old assumption that submission volume roughly tracks researcher effort is getting weaker.
Practical responses may include:
- stricter reproduction requirements
- clearer scope definitions
- better duplicate and template detection
- higher-quality submission gates before human review
- stronger penalties for abusive automated reporting
None of that is free. Every new control adds friction, and too much friction can discourage legitimate researchers. That is the tradeoff: reduce noise without making good-faith reporting harder than it should be for security teams.
A caution for AI in cybersecurity
There is a useful distinction here. AI can assist security work, but assistance is not the same as evidence.
In vulnerability discovery and disclosure, the standard remains the same: a finding must be real, reproducible, and actionable. If AI helps a researcher get there faster, that is one thing. If it mass-produces confident but invalid reports, it shifts cost onto defenders and maintainers.
That matters for buyers evaluating AI security tools as well. Claims about automated discovery are only valuable if they improve validation quality, not just submission quantity. This is a broader caution for AI in cybersecurity.
What to watch next
The next signal will be how Google redesigns the program, if it does. The key question is not whether AI is allowed somewhere in the workflow, but how the program distinguishes credible research from automated noise.
For founders, security teams, and open source maintainers, the takeaway is practical: any workflow that accepts external AI-assisted submissions now needs stronger quality controls up front. If not, the review queue becomes the product’s weakest point.





Comments (0) No comments yet
Want to join this discussion? Login or Register.
No comments yet. Be the first to share your thoughts!