

What Google’s Report Actually Says
Google’s quarterly threat intelligence report, published in September 2026, documents a significant operational shift among several Chinese hacker groups. These actors have moved beyond basic AI prompting and are now deploying AI agents — systems capable of automating multi-step intrusion workflows with minimal human involvement.
The practical consequence is stark: some campaigns are now completed in under six hours. That is a compression of attacker timelines that changes the calculus for defenders.
One group Google has tracked since 2023 has focused specifically on academic, medical, and military research organizations in North America, with a particular interest in proprietary AI research. No victims were named in the report.
The Infrastructure Trick That Makes This Hard to Catch
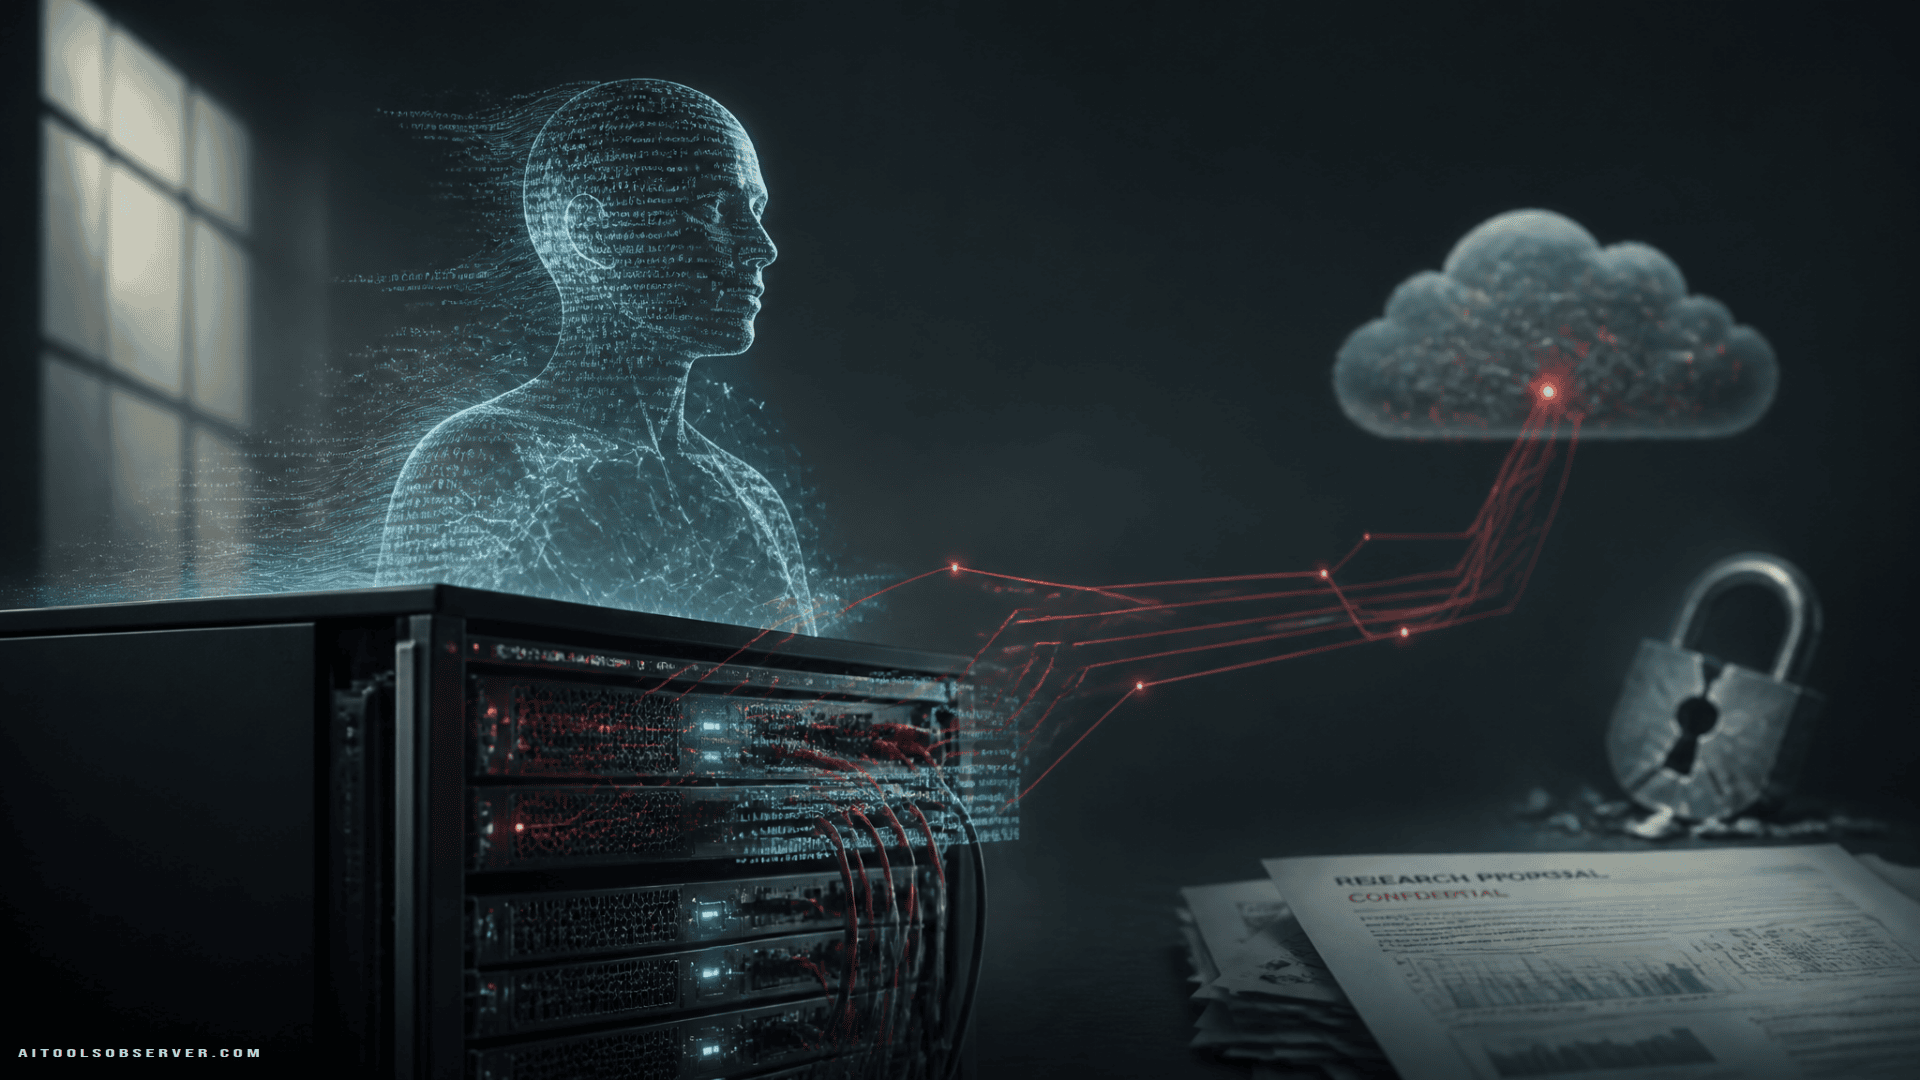
The most technically significant detail in the report is not the use of AI itself — it is where that AI is being run.
Rather than querying commercial AI products, which log activity and apply usage guardrails, these groups compromise unrelated third-party cloud networks and install open-source AI models directly on that stolen infrastructure. The result is a private, unmonitored AI environment that bypasses the content restrictions commercial providers enforce.
John Hultquist, chief analyst at Google’s Threat Intelligence Group, described the logic plainly: they use a hacked third party instead of a commercial option precisely because their activities would be observed on the latter.
This is a deliberate architectural choice, not an improvisation.
Why Open-Source AI Models Are Central to This
The use of open-source models here is not incidental. They are:
- Freely available — no accounts, no billing trails, no terms of service violations to trigger alerts
- Deployable anywhere — including on compromised servers with no vendor oversight
- Unconstrained by guardrails — no content filtering designed to block hacking-related queries
This is a concrete example of the dual-use risk that open-source AI development carries. The same accessibility that makes these models valuable for researchers and developers also makes them useful for actors operating outside legal constraints.
The Broader Trajectory: Toward Autonomous Campaigns
Google states it has not yet observed fully automated hacking campaigns conducted entirely by AI agents. The current pattern is incremental — human operators layering more AI into their workflows, gradually removing themselves from individual tasks.
Hultquist noted that in several cases, groups appeared to be actively building toward autonomous capabilities, attempting to remove humans from the loop on their most critical operations.
No government hacking operation conducted entirely by AI agents has been publicly identified to date. But the direction of travel is clear.
What This Means for the AI Tools Ecosystem
For anyone building on, deploying, or evaluating AI tools — particularly in cloud environments — this report surfaces a few concrete implications worth tracking:
- Cloud infrastructure security is now an AI security issue. Compromised environments can become private AI deployment platforms. This expands the attack surface in ways that traditional endpoint security does not fully address.
- Open-source model deployment needs governance. Organizations running open-source models on shared or cloud infrastructure should treat that deployment as a security-relevant decision, not just an engineering one.
- Proprietary AI research is an active target. If your organization develops or holds AI research assets, the threat profile has materially changed. Academic and medical institutions appear to be in scope, not just defense contractors.
- Guardrails on commercial AI have a real-world function. The fact that attackers are specifically routing around commercial AI providers to avoid guardrails is an indirect validation that those controls have operational value.
The Takeaway
The story here is not that AI is being used for hacking — that has been anticipated for years. The more precise observation is that sophisticated actors are now using stolen infrastructure to run open-source AI in ways that are deliberately designed to be unmonitorable. That combination — agentic automation, open-source models, and third-party cloud compromise — represents a meaningful operational upgrade for adversaries with sufficient resources.
For organizations choosing and deploying AI tools, the question is no longer just “does this tool work?” It is also “does our infrastructure around this tool create exploitable exposure?” Those are different questions, and both now need answers.

Comments (0) No comments yet
Want to join this discussion? Login or Register.
No comments yet. Be the first to share your thoughts!