What Is Bemi?
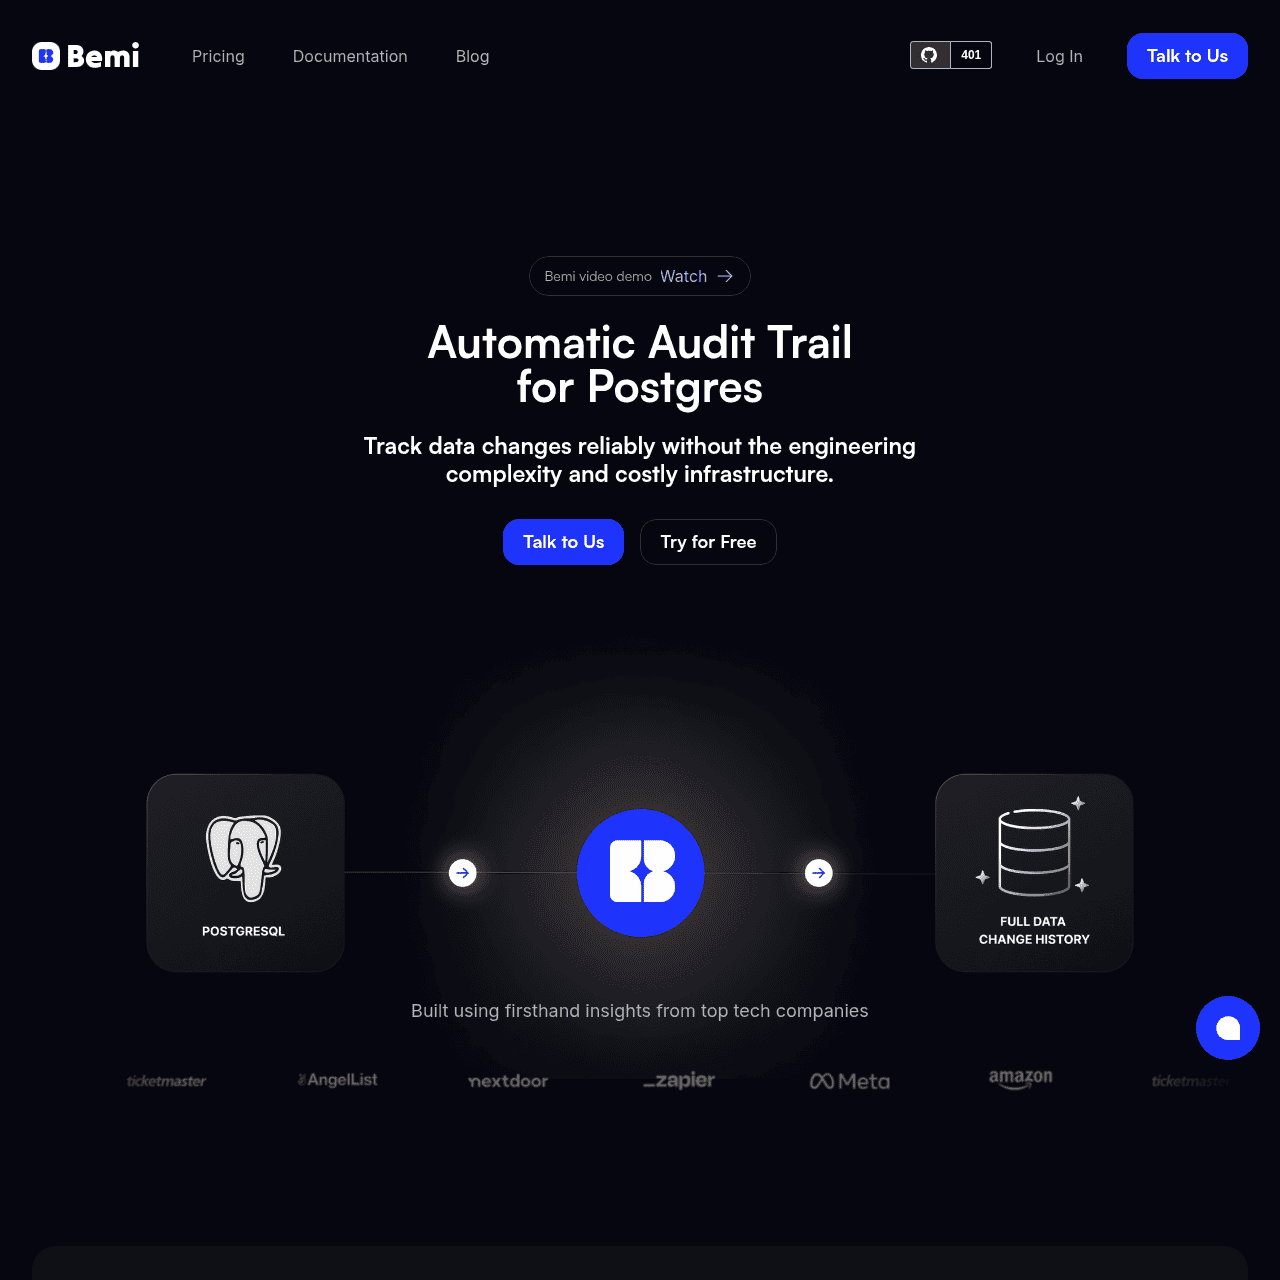
Bemi is a dedicated audit trail and data change tracking platform built specifically for PostgreSQL. It connects to your existing databases and ORMs in minutes, then continuously records every insert, update, and delete as structured, contextual events.
All changes are written to a separate Postgres destination with strong encryption and serverless cluster options, enabling secure retention, time‑travel queries, and incident reconstruction. Designed with security and compliance in mind, Bemi supports TLS encryption, connection pooling, and options for HIPAA and SOC 2 compliance.
Teams can run Bemi as a managed cloud service or self‑host it, and scale to billions of events without building or maintaining custom audit logging infrastructure.
Quick Snapshot
Bemi eliminates the need to build your own audit logging system by automatically capturing every change in your PostgreSQL databases with full context. This gives engineering, data, and compliance teams a reliable history for debugging, analytics, and regulatory audits.
- Works on
-
- Web
- Linux
- Mac
- API
- Other
- Pricing Model
- Subscription
Starting at $19/month — Bemi offers usage‑based subscription plans starting at $19/month for Starter, with higher tiers providing more change volume, databases, users, and security options such as HIPAA and SOC 2. All plans include a 14‑day free trial, support, and a dedicated Slack channel. - Fits on
- Affiliate Program
- We could not identify an affiliate program.
- API Availability
- Bemi has an API available.
- Key Features
-
- Automated, contextual Postgres change tracking
- Secure, encrypted audit trail storage
- Compliance‑ready logging at massive scale
- Audience
-
- backend engineers
- data engineers
- DevOps teams
- SaaS startups
- regulated industry companies
- compliance teams
- security teams
- URL
- https://bemi.io
Screenshot

Key Features of Bemi
Automatic change capture
Continuously records every insert, update, and delete in PostgreSQL as structured, contextual events without modifying existing application logic.
ORM integration
Connects to popular ORMs so teams can start capturing database changes from existing applications in minutes.
Secure event storage
Stores all change events in a dedicated Postgres destination with strong encryption and secure, serverless cluster options.
Compliance ready
Offers TLS encryption, connection pooling, and configuration options to support HIPAA and SOC 2 compliance needs.
Scales to billions
Designed to handle billions of change events with reliable retention and recovery for long‑term audit trails.
Cloud or self‑hosted
Can be deployed as a managed cloud service or self‑hosted, giving teams flexibility to match their infrastructure and security requirements.
Use Cases for Bemi
Regulatory compliance logging
Maintain a complete, encrypted history of database changes to satisfy audit and regulatory requirements such as HIPAA and SOC 2 without custom logging code.
Incident troubleshooting
Quickly reconstruct what changed in the database and when, enabling teams to debug production issues and data incidents with precise historical context.
Data forensics and analysis
Run time‑travel queries on historical change data to analyze how records evolved, investigate anomalies, and support internal investigations.
SaaS customer audit trails
Provide customers with clear, queryable audit trails of changes to their data as a value‑add feature without increasing application complexity.
Security monitoring
Track sensitive data changes with a reliable, append‑only history to detect suspicious modifications and support security reviews.
Frequently Asked Questions
What is Bemi and how does it work?
Bemi is an automatic audit trail and data change tracking platform for PostgreSQL. It connects to your databases and ORMs, then continuously records inserts, updates, and deletes into a secure Postgres destination so you can query historical changes at any time.
Do I need to change my application code to use Bemi?
Bemi is designed to work without altering your application logic. It integrates with your existing PostgreSQL databases and ORMs to capture changes automatically in the background.
Is Bemi suitable for compliance requirements like HIPAA or SOC 2?
Yes. Bemi includes security features such as TLS encryption and offers options to support HIPAA and SOC 2 compliance, making it suitable for regulated industries that need reliable audit trails.
Where does Bemi store audit trail data?
Bemi stores all change events in a dedicated Postgres destination database with strong encryption, separate from your primary application database, to improve security and reliability.
Can Bemi scale to large volumes of database changes?
Bemi is built to scale to billions of change events, so it can support high‑traffic applications and long‑term data retention needs for audit and analytics.
What pricing plans does Bemi offer?
Bemi provides usage‑based subscription plans starting at $19/month, with higher tiers adding more volume, databases, users, and advanced security options, plus a 14‑day free trial.
Bemi · Our Verdict
Bemi offers a focused solution to a notoriously complex problem: reliable audit logging and change tracking in PostgreSQL. By offloading this responsibility from application code and centralizing it in a secure, queryable datastore, it meaningfully reduces operational risk for teams working in regulated or data‑sensitive environments.
The combination of encryption, compliance options, and ORM integration makes it especially compelling for SaaS and enterprise teams that have outgrown ad‑hoc logging.
Bemi ·
-
 Subscription
Narrot
24/7 human-quality support via API
Customer Service Bots - Subscription
Aikido Security
Continuous, developer-first security for everything you build
Risk Assessment - One-Time
BetterLegal
Form your U.S. business in minutes
Legal & Compliance AI - Subscription
LoveHeart (Mana)
AI educator aide for powerful early childhood documentation
Teacher Productivity Tools - Freemium
Xano
AI-ready backend that makes software trustworthy
AI Developer Tools - Your Ad Here
- Freemium
DevAlly
Accessibility compliance for fast-moving product teams
Regulatory Compliance Monitoring - Freemium
Samepage
Your second brain for product management alignment
Task & Project Management