

Policies Exist. Enforcement Does Not.
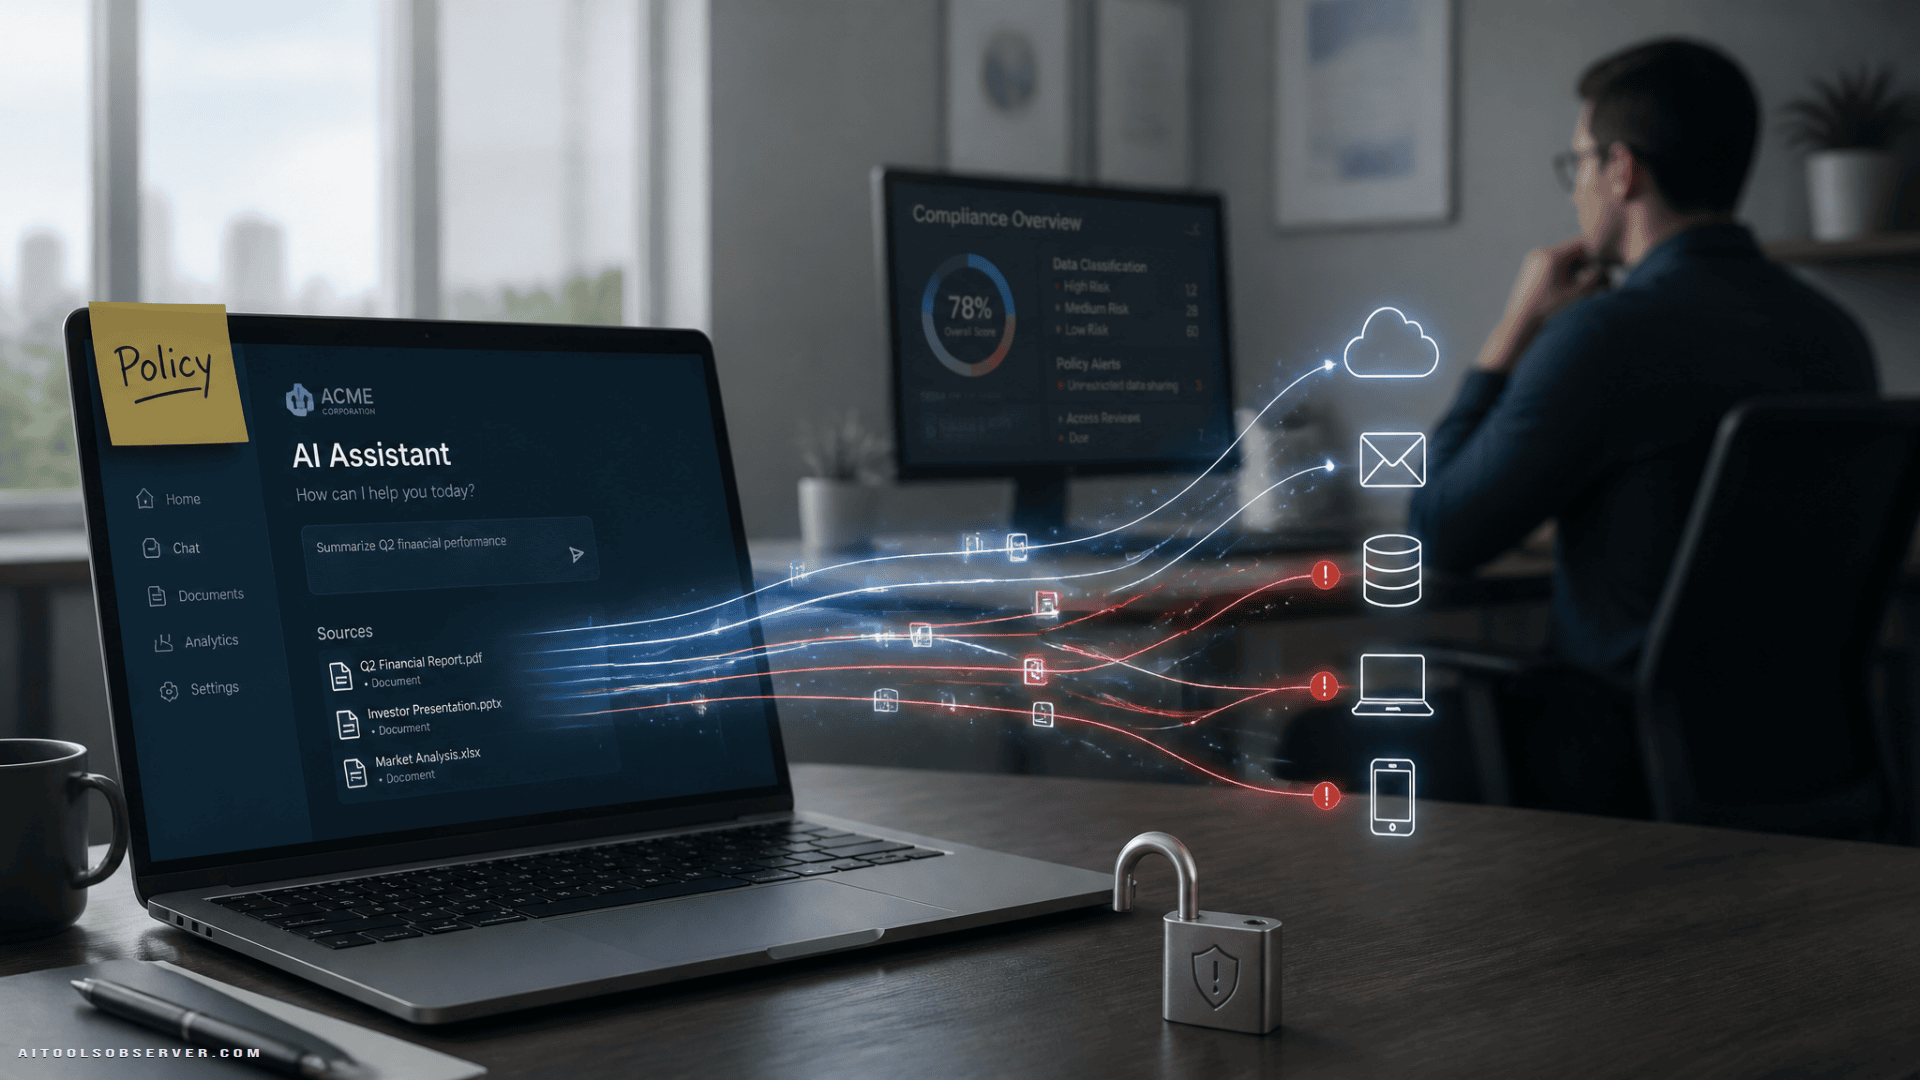
Nearly all organizations surveyed—98%—reported having an AI usage policy in place. But having a policy and enforcing it are two different things.
Only 56% back their policies with comprehensive technical controls. Around 35% have a written policy specifying what employees must not enter into AI prompts, but apply no technical enforcement to it. A policy without enforcement is, in practice, a suggestion.
Darren Williams, founder and CEO of BlackFog, framed the core problem directly: organizations cannot stop at deciding which AI tools employees are allowed to use. They also need to control what information is shared with those tools.
That distinction—tool access versus data flow—is where most governance frameworks currently fall short.
The Speed Problem
Thirty-nine percent of security leaders admitted that AI adoption is moving faster than they can govern it. Among that group, only 27% have comprehensive AI controls in place.
This is a structural tension, not a temporary lag. Business units adopt AI tools to move faster. Security teams need time to assess, classify, and control. The gap between those two speeds is where exposure accumulates.
AI Agents Are Largely Ungoverned
The governance gap widens further when autonomous AI agents enter the picture. More than half of respondents—56%—said that autonomous AI agents acting on behalf of employees fall outside their organization’s existing controls.
In technology and telecoms, that figure rises to 70%.
This is a meaningful risk category. Agents don’t just receive prompts—they take actions, access systems, and move data. Governing what a human types into a chatbox is a different problem than governing what an agent does across an integrated workflow. Most organizations have not yet built controls for the latter.
Shadow AI Remains a Persistent Gap
Only 54% of security leaders said they have the ability to block or restrict unsanctioned AI tools. Around 32% can detect shadow AI use but cannot consistently stop it.
Detection without the ability to act is a partial solution at best. It creates visibility into a problem without the means to resolve it.
What This Actually Means for Security Teams
The BlackFog findings point to three distinct gaps that require separate responses:
- data flow controls — knowing and restricting what information leaves the organization through any AI tool, approved or not
- Policy enforcement — moving from written guidelines to technical controls that make non-compliant behavior harder to execute
- Agent governance — extending existing AI frameworks to cover autonomous agents, which operate with greater autonomy and system access than standard tools
The 48% of organizations that cannot provide any record of what data has left through AI tools represents a significant audit and compliance exposure, independent of whether an incident has occurred.
The practical takeaway is straightforward: approved tool lists are a starting point, not a control. Organizations that treat tool approval as the end of their AI governance work are leaving the most consequential part undone.

Comments (0) No comments yet
Want to join this discussion? Login or Register.
No comments yet. Be the first to share your thoughts!