

Why shadow AI is becoming an endpoint problem
Shadow IT used to mean unsanctioned SaaS accounts. Shadow AI looks messier.
Employees can install AI tools directly on macOS, Windows, and Linux devices, sometimes without going through centralized procurement or security review. That creates a practical problem for IT and security teams: they may not know which AI tools are running, who is using them, what data those tools can access, or how much usage is costing the company.
That matters for a few reasons:
- Sensitive data may be shared into AI tools without clear oversight
- AI-related spend can spread across teams without clear value tracking
- Local and device-level tools are harder to spot than browser-based SaaS
- Compliance reviews get tougher when governance decisions are fragmented across multiple systems
Fleet’s pitch is that AI governance should start where the tools actually run: the endpoint.
What Fleet launched
Based on the available details, Fleet has added AI governance capabilities into its existing device management platform rather than spinning them out as a separate AI security product.
The launch includes several parts that work together.
AI inventory across devices
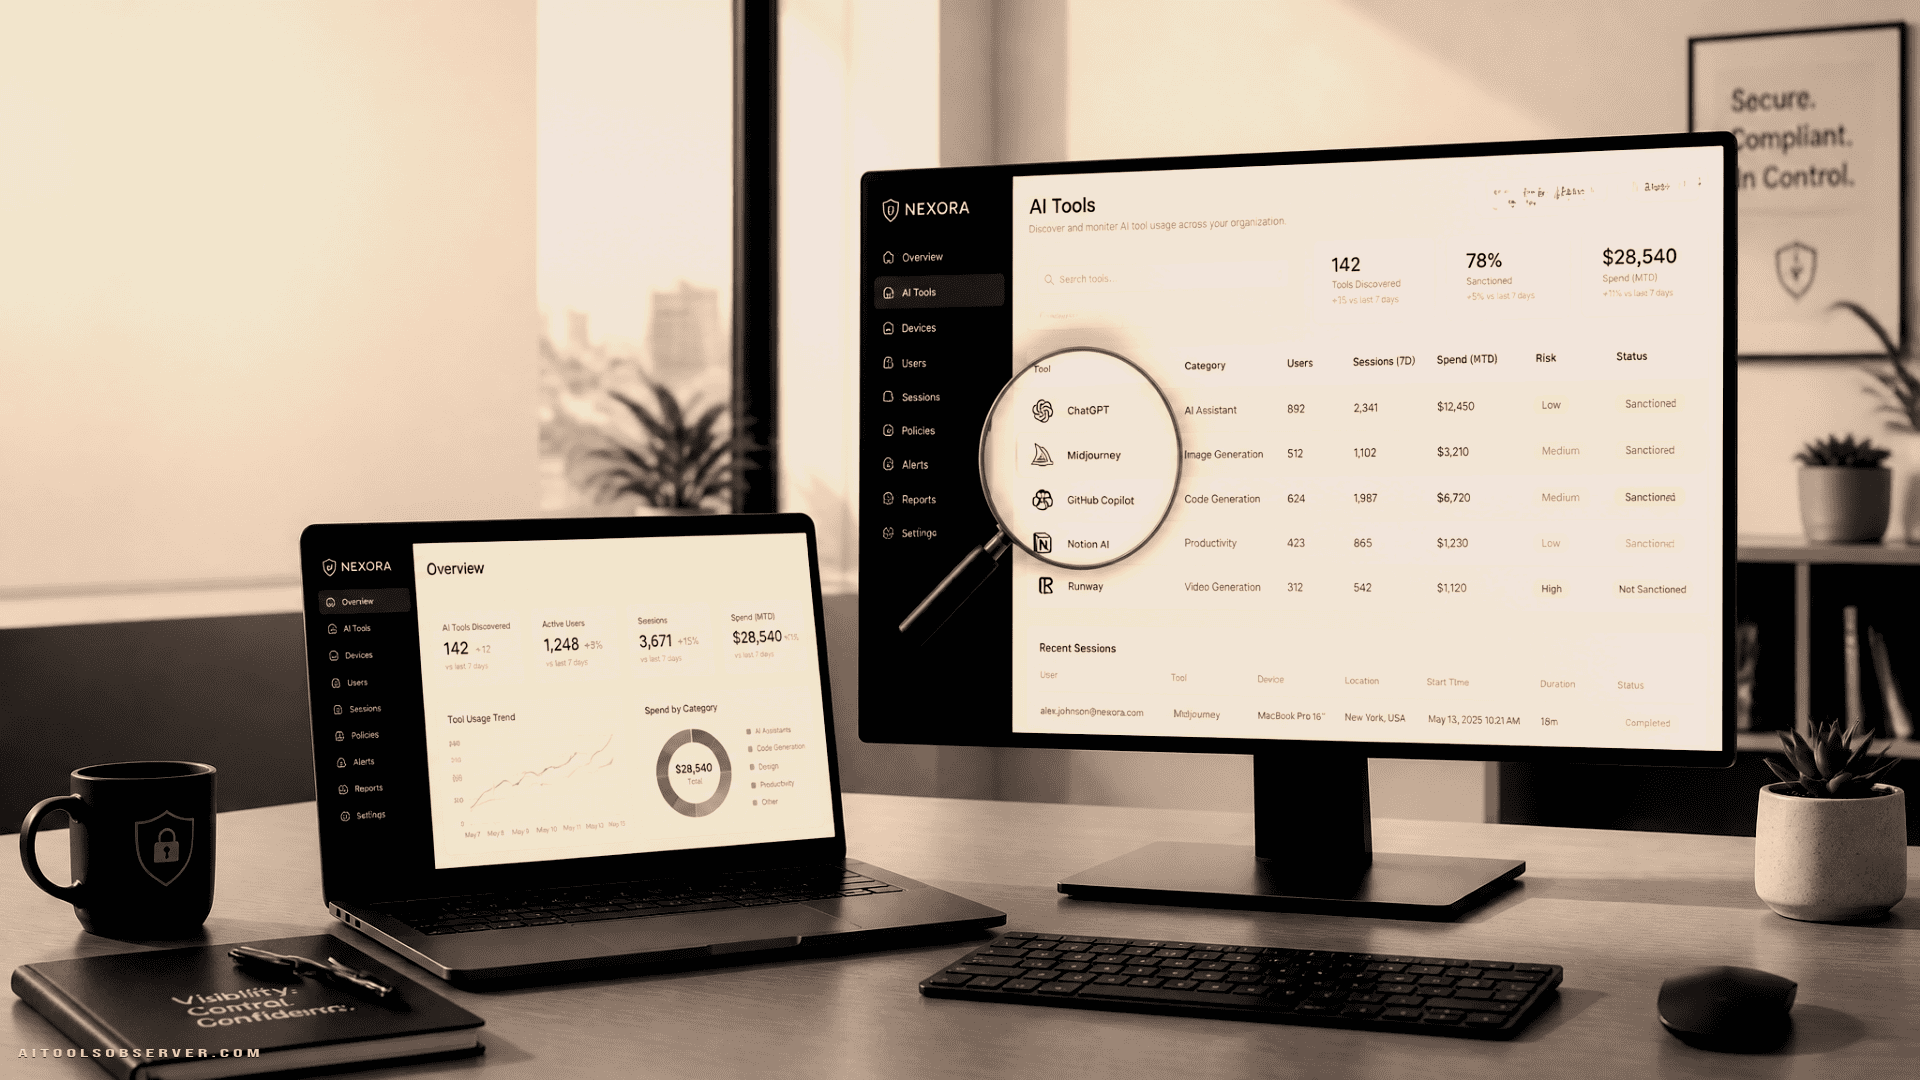
Fleet says teams can see AI tools, agents, skills, plugins, and MCP servers installed across macOS, Windows, and Linux in one view.
That sounds simple, but it solves a core problem. Before governance comes policy, and before policy comes basic visibility. If an organization cannot identify which AI tools exist in its environment, every downstream control becomes guesswork.
The filtering by publisher, version, and device also suggests this is meant for operational use, not just a high-level dashboard.
AI usage and spend tracking
One of the more practical pieces here is usage and spend monitoring. Fleet says teams can track token usage by tool, user, and device.
For IT leaders, that can help answer questions like:
- Which AI tools are actually being used?
- Which teams are driving usage?
- Where is spend increasing?
- Are duplicate tools creating unnecessary cost?
This matters because AI governance is not only about risk. It is also about controlling tool sprawl and understanding whether a growing stack of AI subscriptions and local tools is producing value.
AI session context
Fleet also describes visibility into what users send to AI tools and how those tools respond.
This is the most sensitive part of the launch, and also potentially the most useful for security and compliance teams. If an organization is trying to understand whether employees are sharing source code, customer information, or internal business data with AI systems, session-level context can provide a much clearer picture than a simple installed-app list.
The tradeoff is obvious: deeper visibility tends to raise internal questions about privacy, access controls, and monitoring scope. Organizations adopting features like this will likely need clear internal policies about what is monitored, who can review it, and how long records are retained.
Integrated governance and remediation
Fleet says organizations can use its existing policies, reports, and remediation workflows to identify unmanaged AI tools and decide which agents or applications should remain in the environment.
That may be one of the launch’s strongest positioning points. Security teams already have enough consoles. If AI governance can fit into the same operational workflows used for software, extensions, vulnerabilities, and developer tools, adoption becomes easier.
Instead of adding another standalone layer, Fleet appears to be extending existing device governance processes to include AI.
Auditable controls through IaC and GitOps
The launch also includes auditable controls managed through infrastructure as code and GitOps workflows.
For mature IT and security teams, this matters because governance decisions are rarely just about blocking or allowing a tool. They also need to be:
- Reviewable
- Consistent across operating systems
- Reversible
- Traceable for audits and compliance work
That infrastructure-as-code angle makes the launch more relevant to organizations that already treat endpoint management as part of a broader engineering and security workflow.
Open-source transparency
Fleet emphasizes that organizations can see what data is collected and how, using the same open-source agent already running across the fleet.
In a category like AI governance, where monitoring can quickly become a trust issue, transparency is part of the product story. Open-source visibility will likely appeal most to teams that want to inspect collection methods rather than accept a black-box monitoring approach.
What stands out in this launch
The biggest differentiator is not just “AI governance.” Plenty of vendors are heading toward that label.
What stands out is the framing: AI governance as device management, not just SaaS oversight or AI policy management. That is a useful shift because many AI tools now show up as local software, developer packages, browser extensions, and endpoint agents rather than centralized enterprise apps.
Fleet is also pushing a consolidation angle. The company’s view appears to be that organizations should govern AI in the same place they already manage software, plugins, extensions, vulnerabilities, and device policies.
For buyers, that raises a straightforward question: do you want a separate AI security layer, or do you want AI controls folded into the endpoint systems you already operate?
Who this is for
This launch looks most relevant for organizations already struggling with fast-moving AI adoption across employee devices.
It should be especially useful for:
- IT teams that need a clearer inventory of AI tools across endpoints
- Security teams investigating shadow AI and data exposure risks
- Compliance teams that need auditable governance workflows
- Engineering-heavy companies where developer AI tools spread quickly
- Organizations trying to reduce AI tool sprawl before it becomes unmanageable
It may be less urgent for very small teams with limited endpoint complexity. But once AI usage spreads across departments and devices, endpoint-level visibility becomes much harder to ignore.
Why the free AI inventory tier matters
Fleet says AI inventory and visibility are included in Fleet Free.
That is a smart signal. It lowers the barrier for teams that want to answer the first and most basic question: what AI tools are already running in the environment?
In practical terms, that can help companies start with discovery before they commit to broader governance workflows. And for Fleet, it creates a path from visibility to policy enforcement, spend tracking, and compliance controls.
The bigger trend behind this release
This launch reflects a broader reality: AI adoption is no longer confined to approved enterprise platforms.
It is happening through agents, local models, coding assistants, browser extensions, plugins, and toolchains that individual employees can install faster than central teams can review them. That changes the governance model. Visibility cannot stop at procurement records or sanctioned SaaS logs.
The companies that adapt fastest will likely be the ones that treat AI governance as an operational device-management problem as much as a policy problem.
Final take
Fleet’s AI governance launch is interesting because it focuses on where shadow AI often becomes real: the endpoint.
If your organization is trying to understand which AI tools employees are using, what data is flowing through them, and how to control risk without adding yet another disconnected security product, this release is worth watching. The practical takeaway is simple: before you write more AI policy, make sure you can actually see the AI already running on your devices.
Comments (0) No comments yet
Want to join this discussion? Login or Register.
No comments yet. Be the first to share your thoughts!