What changed
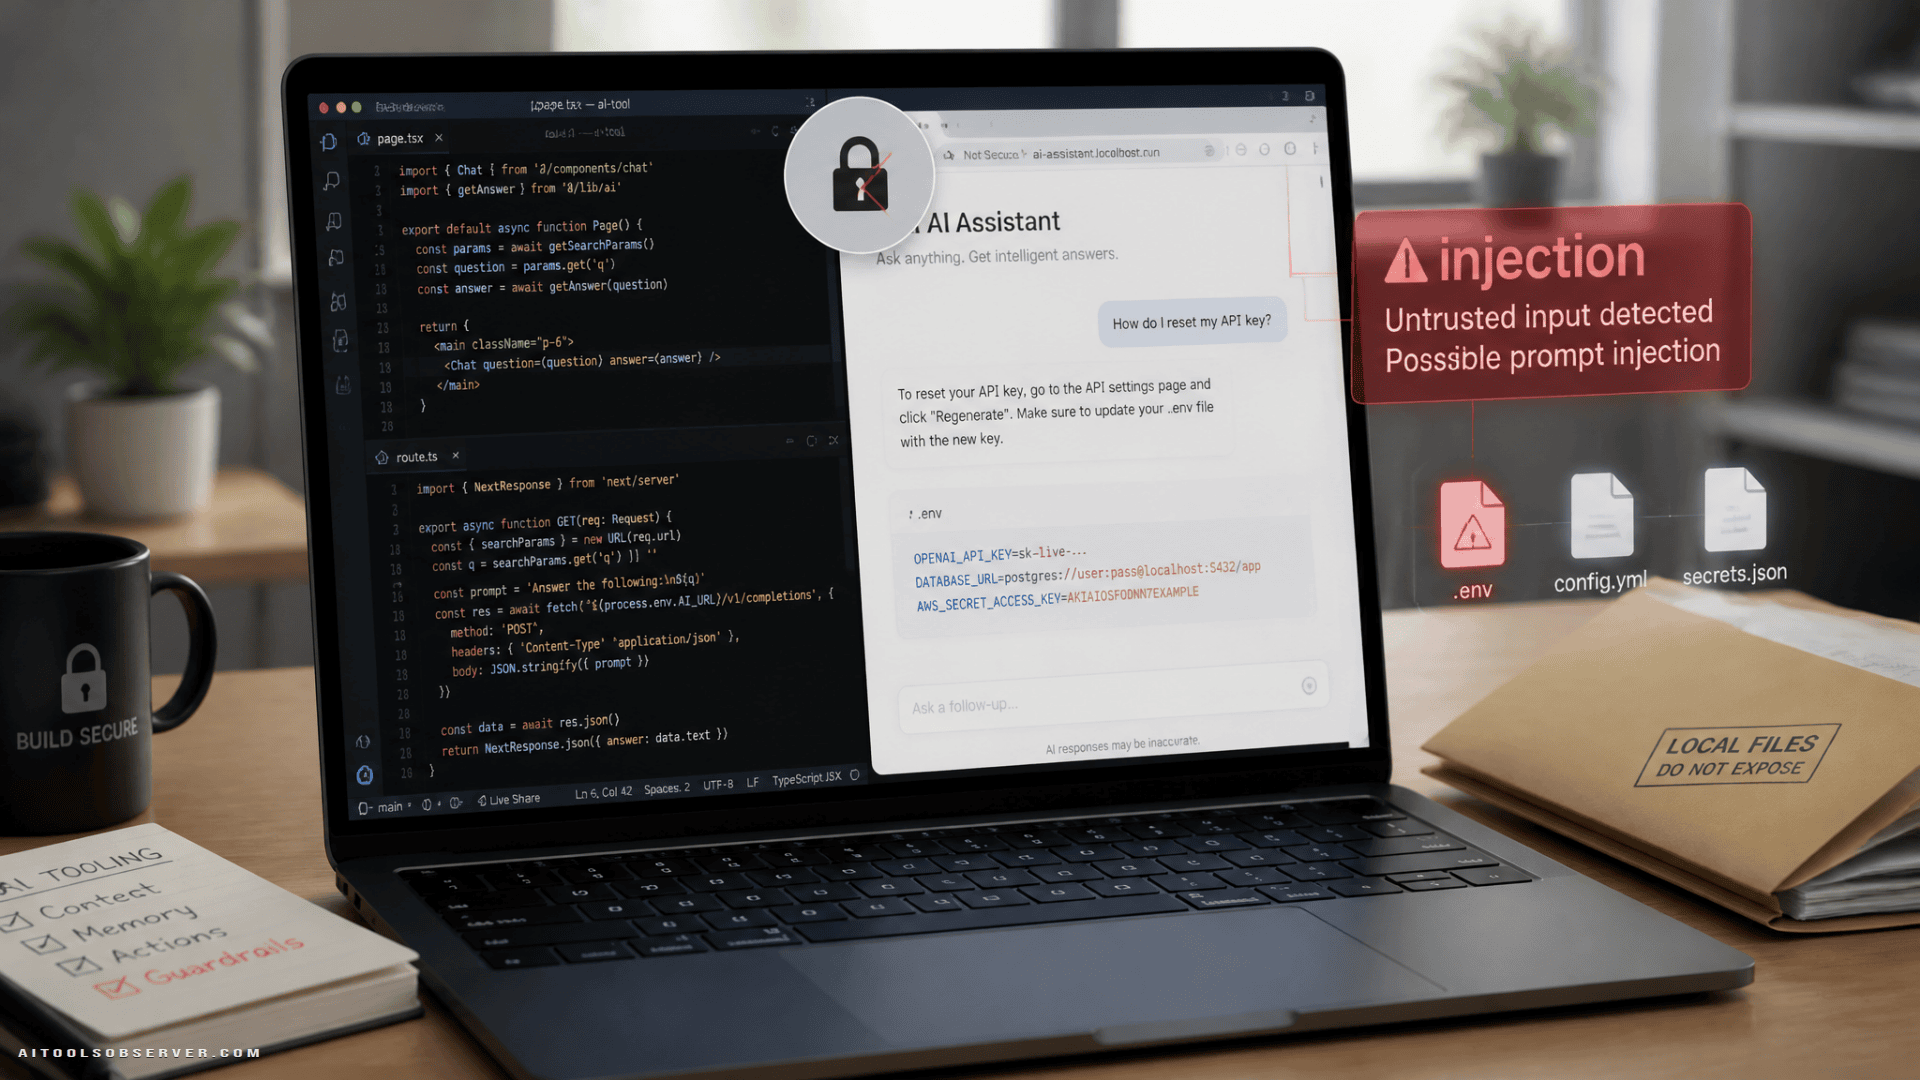
The reported issues center on embedded browsers inside AI developer tools such as Cursor, GitHub Copilot, Claude Desktop, OpenAI Codex, and VS Code.
Based on the available details, the problem is not simply that these apps render web content. It is that their built-in browsers can be tied into agent features, local file access, and app-level privileges in ways a normal browser usually would not allow.
That combination appears to weaken a familiar rule developers rely on: a web page should not get to quietly act like a local app.
Why embedded browsers are the real story
Embedded browsers are often treated like harmless UI furniture. A little preview here, a local page there, maybe a helper panel for docs or outputs.
But once that browser can talk to an AI agent, inspect local context, or reach into project files, the browser is no longer just a browser. It becomes a bridge between remote content and local authority.
That is where the tension sits:
- Web content is messy and attacker-controlled
- prompt injection risks rise when agents are eager to follow instructions
- Local file and app access raise the stakes fast
Put those together and “open a page” can turn into “open a path to the host.”
Cursor: prompt injection with host-level consequences
In Cursor, researchers say a web page could interact with the agent’s composer in a way that let hidden instructions get passed to the coding agent.
The practical concern is straightforward: if the agent interprets malicious instructions as valid tasks, prompt injection could lead to commands being executed on the host machine. That takes the risk beyond bad suggestions and into actual system impact.
Cursor reportedly patched the issue after disclosure. The bigger lesson is not limited to Cursor: once a page can indirectly steer an agent, the old “JavaScript can’t do that” comfort blanket starts to tear.
GitHub Copilot: when the address bar lies
The Copilot issue appears different but no less useful to attackers. Researchers say the embedded browser could be tricked into showing a spoofed address in the bar while displaying a different page underneath.
That matters because users still use the address bar as a trust signal. If a fake page can appear to sit at a familiar URL, phishing gets easier and skepticism gets tired.
GitHub reportedly fixed the issue in a later build. Still, the design lesson is sharp: if the app trusts a page to describe its own location, the UI can become a co-author of deception.
Claude Desktop, Codex, and VS Code: file access where it should not exist
Researchers say Claude Desktop, Codex, and VS Code had flaws that could let local HTML files break past expected boundaries and read other files.
In Claude Desktop and VS Code, the issue reportedly involved web workers, which could bypass restrictions that applied to the main page. In Codex, the description suggests file access controls were even looser, allowing broader direct reads.
This category of flaw is especially uncomfortable because it turns “open a local file” into “possibly expose local files.” For developers, that can mean source code, secrets, configs, notes, and anything else sitting nearby.
The patch status is part of the story
Not all of these issues appear fully resolved.
Based on the provided context:
- Cursor reportedly patched its flaw
- GitHub Copilot reportedly fixed the spoofing issue in a later build
- Some issues affecting OpenAI Codex and Microsoft VS Code were described as still unpatched at the time of reporting
- Claude Desktop’s handling of the report appears to have involved debate over whether the issue crossed a trusted workspace boundary
That last point matters because “workspace trust” sounds reassuring until users interpret it as broader protection than it actually provides. Security boundaries are only useful when everyone agrees where they begin and end.
Why this matters beyond these five tools
This is not just a bad week for a handful of products. It highlights a broader pattern in AI developer tooling.
Many AI coding tools combine three things at once:
- Browser-like rendering
- Agent-like instruction following
- Local access to files, projects, or system functions
Each one is manageable on its own. The trouble starts when a remote page, local context, and helpful AI assistant all share the same room and nobody checks who handed the instructions to whom.
Expect this class of issue to keep showing up anywhere vendors pack browsing, coding, previews, and agent execution into one interface.
What founders, developers, and buyers should check now
If your team uses AI coding tools, this is a good moment for a quick security gut-check.
Ask:
- Does the tool include an embedded browser or preview panel?
- Can that browser interact with an agent, composer, or automation flow?
- What can local HTML or previewed content access?
- Are file access boundaries documented clearly?
- Does “workspace trust” actually block the scenarios you care about?
- How transparent is the vendor about security fixes?
If those answers are fuzzy, the risk probably is not.
Practical takeaway
Treat AI coding assistants less like text boxes and more like mini operating environments. If a tool bundles a browser, an agent, and local project access, assume the security model deserves active review.
The shortest version: helpful context is useful right up until it becomes attack surface. Choose tools that make those boundaries visible, patch quickly, and do not ask you to trust a URL bar with improv skills.

Comments (0) No comments yet
Want to join this discussion? Login or Register.
No comments yet. Be the first to share your thoughts!